Exporting Passkeys Safely
Passkeys are public-key credentials tied to a relying party (a website or app) and an account. When you sign in, your device proves possession of a private key without sending the key to the website. Exporting credentials usually means creating a backup or transfer path for those passkeys so you do not strand your account after a device change.
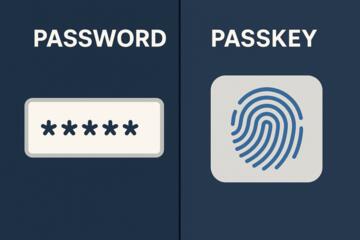
In practice, passkeys behave differently from passwords. A password export is a text file; a passkey export is often a set of cryptographic credentials that must be re-registered on the new device. Some ecosystems support direct transfer; others require re-creation through account settings. If you treat passkeys like a downloadable “password list,” you end up with a migration that looks successful but fails at login time, which is where the pain starts.
Start by listing every service that uses passkeys, then decide what “export” means for each one. For example, a password manager may store passkeys for some sites, while a separate device transfer feature may move passkeys for others. I keep a simple spreadsheet with columns for “transfer supported,” “re-registration required,” and “recovery method,” because the details vary by platform and version.
Common Failure Points
People often get the dependencies wrong. Passkeys depend on a specific account identity at the relying party, a compatible authenticator (phone, security key, or platform authenticator), and a recovery path if the authenticator is lost.
One frequent mistake is exporting only the “account login” without the passkey. For instance, you might export recovery codes for a site, but the passkey itself stays on the old device. Another mistake is assuming that a passkey export from one password manager or browser will automatically cover every site. Many tools store passkeys only for the accounts they manage, and some sites require a fresh registration step even when a backup exists.
Device migration adds another layer. If you switch phones without transferring passkeys first, the new device may not have the private keys needed for existing passkeys. Even when the new device can create new passkeys, it cannot authenticate with the old ones unless you re-register them on the new device through the account’s passkey management page.
Finally, recovery settings get overlooked. If a site offers both passkeys and a fallback method (like SMS, email, or security keys), the fallback can become the only way back in after a failed migration. That fallback may have rate limits or verification delays, so you want it tested before you need it. On my side, I once found that a recovery email change request took 24–48 hours, which made a “quick” migration plan turn into a waiting game.
Plan Your Export Path
Map Services To Transfer Options
Write down each relying party that uses passkeys and check its passkey management and recovery options. Many services provide a “Passkeys” or “Security” section where you can add a new passkey and remove old ones. If the site supports adding a passkey while logged in, you can treat migration as a re-registration workflow rather than a literal export.
For device-to-device transfer, rely on the platform’s documented passkey transfer feature when available. For example, Apple’s iCloud Keychain and Google Password Manager have different behaviors and scopes, and they do not always cover every authenticator type. If you see a setting like “Passkeys” inside your password manager, check whether it includes “sync” and whether it covers third-party browsers. I recommend verifying on a single low-risk site first, because the UI can differ between app versions (I saw this between iOS 17.6 and 18.0 betas, and it was annoying).
Use Security Keys As A Backstop
For accounts that matter, add at least one external security key that supports passkeys (commonly via FIDO2/WebAuthn). A security key acts as an authenticator independent of your phone’s storage. If your phone is lost, you can sign in using the security key and then register new passkeys on your replacement device.
When you add a security key, label it in your notes and store it somewhere you can access. Many services allow multiple passkeys per account, so you can keep one key at home and one in a separate safe location. The realistic outcome you want is not “perfect portability,” but “account recovery without waiting for support.”
Re-Register Passkeys After Login
If you still have access to the old device and can sign in to the account, the most reliable method is re-registration. Log in, open the site’s passkey management page, and add a new passkey using the new device or a password manager. Then remove the old passkey only after you confirm you can sign in from the new device.
Use a short test window. For example, after adding the new passkey, sign out and sign back in immediately. If the site supports it, also test from a different browser or app context. This catches cases where the passkey is available in one environment but not another, which happens when a browser uses a different credential store.
Test Recovery Before You Switch Devices
Before you migrate, test the recovery path without breaking the account. Confirm you can receive verification emails, that your phone number is current, and that you can complete a login challenge. Some services throttle repeated attempts, so do the test once and then stop.
Also check whether your passkey export is actually a transfer. If a tool says “sync passkeys,” confirm it is enabled and that the relying party appears in the tool’s passkey list. If you see only “passwords” but not “passkeys,” you may have a false sense of coverage. On one account, my password manager showed saved credentials but not passkeys until I enabled a specific “passkeys” toggle in settings (the label differed by version).
Educational Case Examples
Phone Upgrade With Sync Enabled
A person upgrades from one phone to another and keeps the same account login. They verify that passkeys sync is enabled in their platform password manager, then they open the site’s passkey management page while still logged in. They add a new passkey on the new phone, sign out, and sign back in on the new phone. Only after the test succeeds do they remove the old passkey.
The key detail is that they do not rely on “export” alone. They treat passkey migration as a verification loop: add, sign out, sign in. That loop catches mismatches between credential stores and relying party expectations.
Lost Phone With Security Key
Another scenario involves a lost phone. The person uses a previously registered security key to sign in to the account. After regaining access, they add passkeys for the replacement phone and remove the old passkey entries if the service supports it. They also update recovery email and phone number to prevent future lockouts.
This scenario works because the security key is an independent authenticator. Without it, the person would likely depend on email or phone verification, which can take time and may require additional identity checks.
Checklist For A Safe Export
| Approach | What You Get | Typical Limit | Best Use |
|---|---|---|---|
| Platform passkey sync | Passkeys appear on another device signed into the same ecosystem | Coverage varies by browser/app and relying party | Convenient migration when you keep access to the account |
| Password manager passkeys | Passkeys stored and surfaced through the manager’s credential flow | Not every site and authenticator type behaves the same | Centralizing credentials across compatible browsers |
| Security key backstop | Independent authenticator for sign-in and re-registration | Requires you to register the key ahead of time | Recovery plan for lost device scenarios |
| Re-register after login | New passkeys created on the new device | Depends on keeping account access during migration | Most reliable when you can still sign in |
Step-by-step checklist you can follow before a device switch:
- List every relying party that uses passkeys and note your current recovery methods.
- On the old device, sign in to each account and open the passkey/security settings page.
- Add a new passkey on the new device (or via your password manager) while you still have access.
- Sign out and sign back in from the new device for each account.
- Only then remove old passkeys, if the service offers removal, and confirm you can still sign in.
- Register at least one security key for high-value accounts if you can do it before migration.
- Test email/phone recovery once, then stop to avoid lockouts from repeated attempts.
Common Mistakes To Avoid
One mistake is treating “export” as a single action. Passkeys rarely export as a universal file you can import anywhere. Instead, you typically transfer within an ecosystem or re-register through each relying party’s account settings.
Another mistake is removing old passkeys too early. If you delete the only working authenticator before testing sign-in on the new device, you force recovery workflows that can take hours or days. A safer sequence keeps both passkeys active until the new one passes a sign-out/sign-in test.
People also misread browser prompts. A browser may offer to create a passkey, but the credential store used by that browser can differ from another browser on the same device. If you create passkeys in one browser and later sign in using another, the passkey might not appear where you expect.
Finally, avoid “credential sharing” habits. Passkeys are designed so the private key stays with the authenticator. If a tool asks you to copy private material, stop and verify what it is actually doing, because passkey flows should not require you to export secrets in plain text.
FAQ
Can I Export Passkeys Like Passwords?
Most passkey systems do not export as a reusable text or file format. Migration usually happens through ecosystem sync or by re-registering passkeys in each account’s security settings.
What Happens If I Lose My Phone?
If you registered a security key or have another authenticator, you can sign in and add new passkeys. Without a backstop, you rely on the site’s recovery methods, which may include email or phone verification.
Will Passkeys Sync Across Browsers?
Sync depends on the platform and the credential store. A passkey created in one browser may not appear in another if the browser uses a different authenticator integration.
Do I Need To Re-Register After Migration?
Often yes. Even when passkeys sync, the safest approach is to add a new passkey on the new device and test sign-in before removing the old one.
How Many Security Keys Should I Register?
For high-value accounts, at least two is common: one for daily use and one stored separately. The exact number depends on your risk tolerance and how quickly you can recover if a key is lost.
Author's Insight
Passkeys rely on public-key cryptography and an authenticator that holds the private key. That design reduces password theft risk, but it changes migration from “copy and paste” to “transfer or re-register.” The most reliable export strategy treats each relying party as its own credential lifecycle: add a new passkey while logged in, then verify sign-in from the new device.
Because platform behaviors vary by browser and app version, testing matters more than reading a single checklist. If you can, register a security key for accounts where recovery delays would cause real disruption, then keep recovery email and phone current.
Key Takeaways
- Passkeys usually do not export as a universal file; migration is typically sync or re-registration per account.
- Keep old passkeys until the new device passes a sign-out/sign-in test.
- Use security keys as an independent recovery path for high-value accounts.
- Verify recovery methods once before switching devices, since delays can be part of the process.