Synced Vs Device-Bound
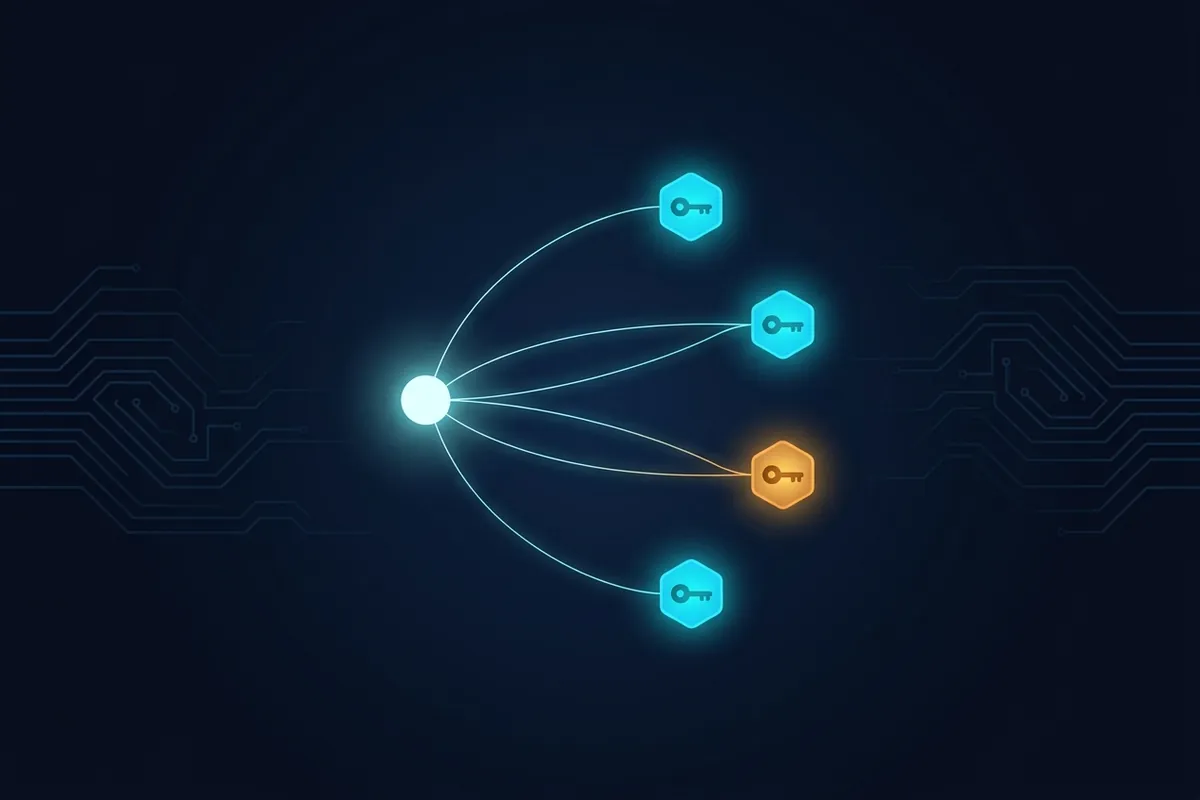
Passkeys use public-key cryptography so a service can verify you without receiving a reusable password. A passkey is tied to an account on a relying party (for example, a patient portal) and to one or more authenticators (devices or password managers). The difference between synced and device-bound passkeys comes from where the private key lives and how it moves across your devices.
With synced passkeys, the private key is stored in a cloud-backed password manager and replicated to other signed-in devices. With device-bound passkeys, the private key stays on a single authenticator and does not replicate to other devices. Both approaches rely on WebAuthn and related standards, but the key storage and recovery story changes the risk profile.
Example: you log into a telehealth app on your phone, then later try the same account on a laptop. If the passkey is synced, the laptop can often discover the passkey through the password manager sign-in. If the passkey is device-bound, the laptop usually cannot use it unless you created a separate passkey on that laptop or you have a recovery path that re-creates the credential.
One practical aside: on macOS Sonoma 14.x, passkey prompts in Safari often route through the system keychain and the password manager integration, which makes synced behavior feel “automatic” until you sign out of the account that performs the sync.
Main Pain Points
People often assume that “passkey” means “works everywhere,” then get blocked when the private key never left the original device. Another common misunderstanding is mixing up account sync with credential sync: signing into the same email account does not guarantee passkey replication unless the passkey provider is the same and the device is enrolled.
Device-bound passkeys create a dependency on the authenticator’s hardware security module or secure enclave. If you replace a phone, factory reset, or lose biometric access, the passkey may become unusable. Some platforms offer recovery mechanisms, but those mechanisms vary by vendor and by whether you used a passkey sync feature during setup.
Synced passkeys introduce a different dependency: the cloud sync account and its security controls. If you lose access to the password manager account, the passkeys may not be available on new devices. If you change phones but keep the same sync account session, the passkeys often reappear after a short sync delay, but the exact timing depends on background sync behavior and device connectivity.
Another aside from real-world friction: many users create a passkey on one device, then later disable “password manager sync” in browser settings. The passkey still exists on the original device, yet the relying party may show “no passkey found” on the new device, which feels like a service outage even when the service is fine.
Solutions And Advice
Choose Based On Your Devices
Start by listing the devices you actually use for the same accounts: phone, laptop, tablet, and any shared computer. If you regularly sign in from multiple devices, synced passkeys reduce friction because the private key can be replicated to each enrolled device. If you mostly use one device for sensitive accounts, device-bound passkeys reduce the number of places the credential can appear, which can simplify your threat model.
For health-related accounts, consider the access pattern: patient portals and telehealth apps are often used on a phone and a desktop browser. If you expect to switch between them, synced passkeys usually reduce lockouts caused by “new device, no passkey.” If you expect to keep one dedicated device for those accounts, device-bound passkeys can work well, but you need a recovery plan for device loss.
Set Up Recovery Before You Need It
Before you rely on passkeys for a critical account, confirm the account’s recovery options. Many services still offer fallback methods such as backup codes, email verification, or SMS, but the availability varies by provider and region. If the service offers “add another passkey” or “register a new authenticator,” do it while you still have access to the original device.
Practical target: register at least two authenticators for high-stakes accounts—one primary device and one secondary device. If your passkey provider supports it, create a second passkey on a laptop you control. If you cannot, store backup codes in a secure place and test the recovery flow once, even if it feels tedious.
Verify Where The Key Lives
When a browser or password manager offers passkey creation, look for cues about sync. Some interfaces show whether passkeys are stored in a password manager that syncs across devices. If you see only device-local options, treat the credential as device-bound even if the UI uses the word “passkey” generically.
Tooling detail: in Chrome, passkey management often appears under password manager settings and can be tied to your Google account sign-in. In Firefox, passkeys may rely on the platform’s credential manager. The key point is not the brand name; it is whether the private key is replicated to other devices under a sync account you control.
Plan For Phone Changes
When you change phones, the safest sequence is: keep the old device available until the new device has passkeys working on a test account. If you are moving from one OS to another, confirm that the passkey provider supports cross-platform sync. If you are using device-bound passkeys, you may need to re-register passkeys on the new device.
A mild frustration that shows up often: users transfer data from the old phone to the new one, then discover that the passkey did not transfer because it was never part of the data migration. The secure enclave credential usually cannot be exported, so “phone backup restore” does not always recreate the passkey.
Case Examples
Telehealth On Phone Then Laptop
Scenario: A patient uses a telehealth app on an iPhone and later logs in from a Windows laptop. The account supports passkeys, and the patient created the passkey using a synced password manager. After signing into the same password manager on the laptop, the passkey appears and login succeeds with a biometric prompt. When the patient signs out of the password manager sync account, the passkey no longer appears on the laptop, and the patient must use the service’s fallback recovery method.
Lost Phone With Device-Bound Passkey
Scenario: A user registers a passkey on a single Android phone using a device-local authenticator mode. The user later loses the phone and has no backup codes and no secondary authenticator registered. The relying party cannot verify the passkey because the private key is not available. Recovery depends on the service’s fallback options, so the user must use email verification or other account recovery steps, then re-register passkeys on a new device.
Comparison Checklist
| Decision Factor | Synced Passkeys | Device-Bound Passkeys | What To Check |
|---|---|---|---|
| Where the private key lives | In a cloud-backed password manager and replicated to enrolled devices | On a single authenticator (secure hardware) and not exported | Whether your passkey provider syncs across devices under a login |
| Device replacement | Often works after you sign into the same sync account | Usually requires re-registering on the new device | Whether the service supports adding a new passkey quickly |
| Recovery if you lose access to the sync account | Passkeys may not appear on new devices until sync is restored | Recovery depends on fallback methods and whether another authenticator exists | Whether backup codes or secondary authenticators exist |
| Cross-device login friction | Lower when devices are enrolled and sync is active | Higher unless you register passkeys on each device | Whether you regularly log in from multiple devices |
Step-by-step checklist for a health account:
- Register a passkey on your primary device.
- Register a second passkey on a secondary device you control, or confirm synced replication is active.
- Open the account’s security settings and confirm fallback recovery methods (backup codes, email verification, or other options).
- Test sign-in on a different device before you need it, even if it takes 2–3 minutes.
- If you change phones, keep the old device until the new device can sign in with the passkey.
Common Mistakes
One mistake is treating passkeys as a replacement for account recovery. Passkeys reduce phishing risk, but they do not remove the need for recovery paths when you lose an authenticator or a sync account. Another mistake is creating only one passkey for an account that you cannot afford to lose access to.
People also misjudge how browser settings affect passkey availability. If a browser disables password manager integration, the passkey prompt may not find synced credentials even though the credentials exist in the password manager. Users then blame the service, when the issue is the credential discovery layer.
A subtler error involves shared devices. If you use a shared computer at work or with family, device-bound passkeys can reduce credential spread, but synced passkeys can still appear if the password manager is signed in. That can lead to confusing prompts and, in some cases, account mix-ups.
Finally, users sometimes assume that “passkey created” means “passkey replicated.” Sync can take time, and background sync can pause when battery saver or network restrictions apply. If a passkey does not appear immediately, waiting a short period and checking sync status is more reliable than repeatedly re-registering credentials.
FAQ
Do Synced Passkeys Work Across Browsers?
They often work across browsers on the same device because the credential manager and password manager integration expose the passkey. Cross-browser behavior depends on platform support and whether the password manager sync is active.
Can A Device-Bound Passkey Be Exported?
Device-bound passkeys are designed not to be exported in a usable form. Recovery typically requires re-registering the passkey on a new authenticator or using the service’s fallback recovery methods.
What Happens After I Reset My Phone?
A device-bound passkey usually disappears because the secure hardware credential is erased. A synced passkey may reappear after you sign into the same sync account and the device finishes credential sync.
Do Passkeys Remove Account Recovery Steps?
No. Services still need recovery paths for cases like lost devices, disabled biometrics, or lost access to the sync account. You should check backup codes and secondary authenticator options before relying on passkeys alone.
Are Passkeys Safer Than Passwords For Health Portals?
Passkeys reduce phishing and credential reuse because the login uses cryptographic proof tied to the relying party. The safety outcome depends on correct setup, device security, and whether you keep recovery options available.
Author's Insight
Synced and device-bound passkeys differ mainly in where the private key is stored and how it is replicated. WebAuthn and related credential manager behaviors determine how relying parties discover credentials, while platform security controls determine whether keys can move between devices. For health accounts, the practical decision hinges on your device replacement pattern and your recovery options, not on the passkey label alone. A careful setup—two authenticators plus a tested fallback—reduces lockouts more than choosing one passkey type by preference.
Key Takeaways
- Synced passkeys replicate credentials through a password manager sync account; device-bound passkeys stay on one authenticator.
- Device-bound passkeys reduce credential spread but increase lockout risk after device loss unless you register another authenticator.
- Synced passkeys reduce cross-device friction but depend on the sync account and its security controls.
- Register at least two authenticators for high-stakes accounts and verify fallback recovery methods before you need them.